Loading
Find the Gap Bug Bounty for Government
Korea's largest bug bounty platform for government, public administration, and educational institutions.
Registered on Korea's Digital Service Mall Easy adoption for government, public, and educational institutions
Adopt Find the Gap directly through the Digital Service Mall without a complex procurement process.
Triple Government Certification
K-Innovative Product (Type 1)
Designated as a government innovative product by the Procurement Policy Review Committee. Public institutions can sign private contracts for 3 years, with trial-purchase programs and purchase indemnity applied.
CSAP Standard Level Certified
Achieved the highest cloud security certification required for public-sector SaaS adoption (CSAP-2026-022, valid through June 2031). Institutions can adopt immediately without a separate security review.
Registered Excellent Security Technology
Officially registered as an excellent information security technology designated by the Ministry of Science and ICT.
Blind Spots in Periodic Security Audits
Who is responsible for new vulnerabilities that emerge the day after an audit ends? Complete a public security posture faster than any attack with Find the Gap Bug Bounty, monitored 24/7 in real-time by 7,700 ethical hackers.
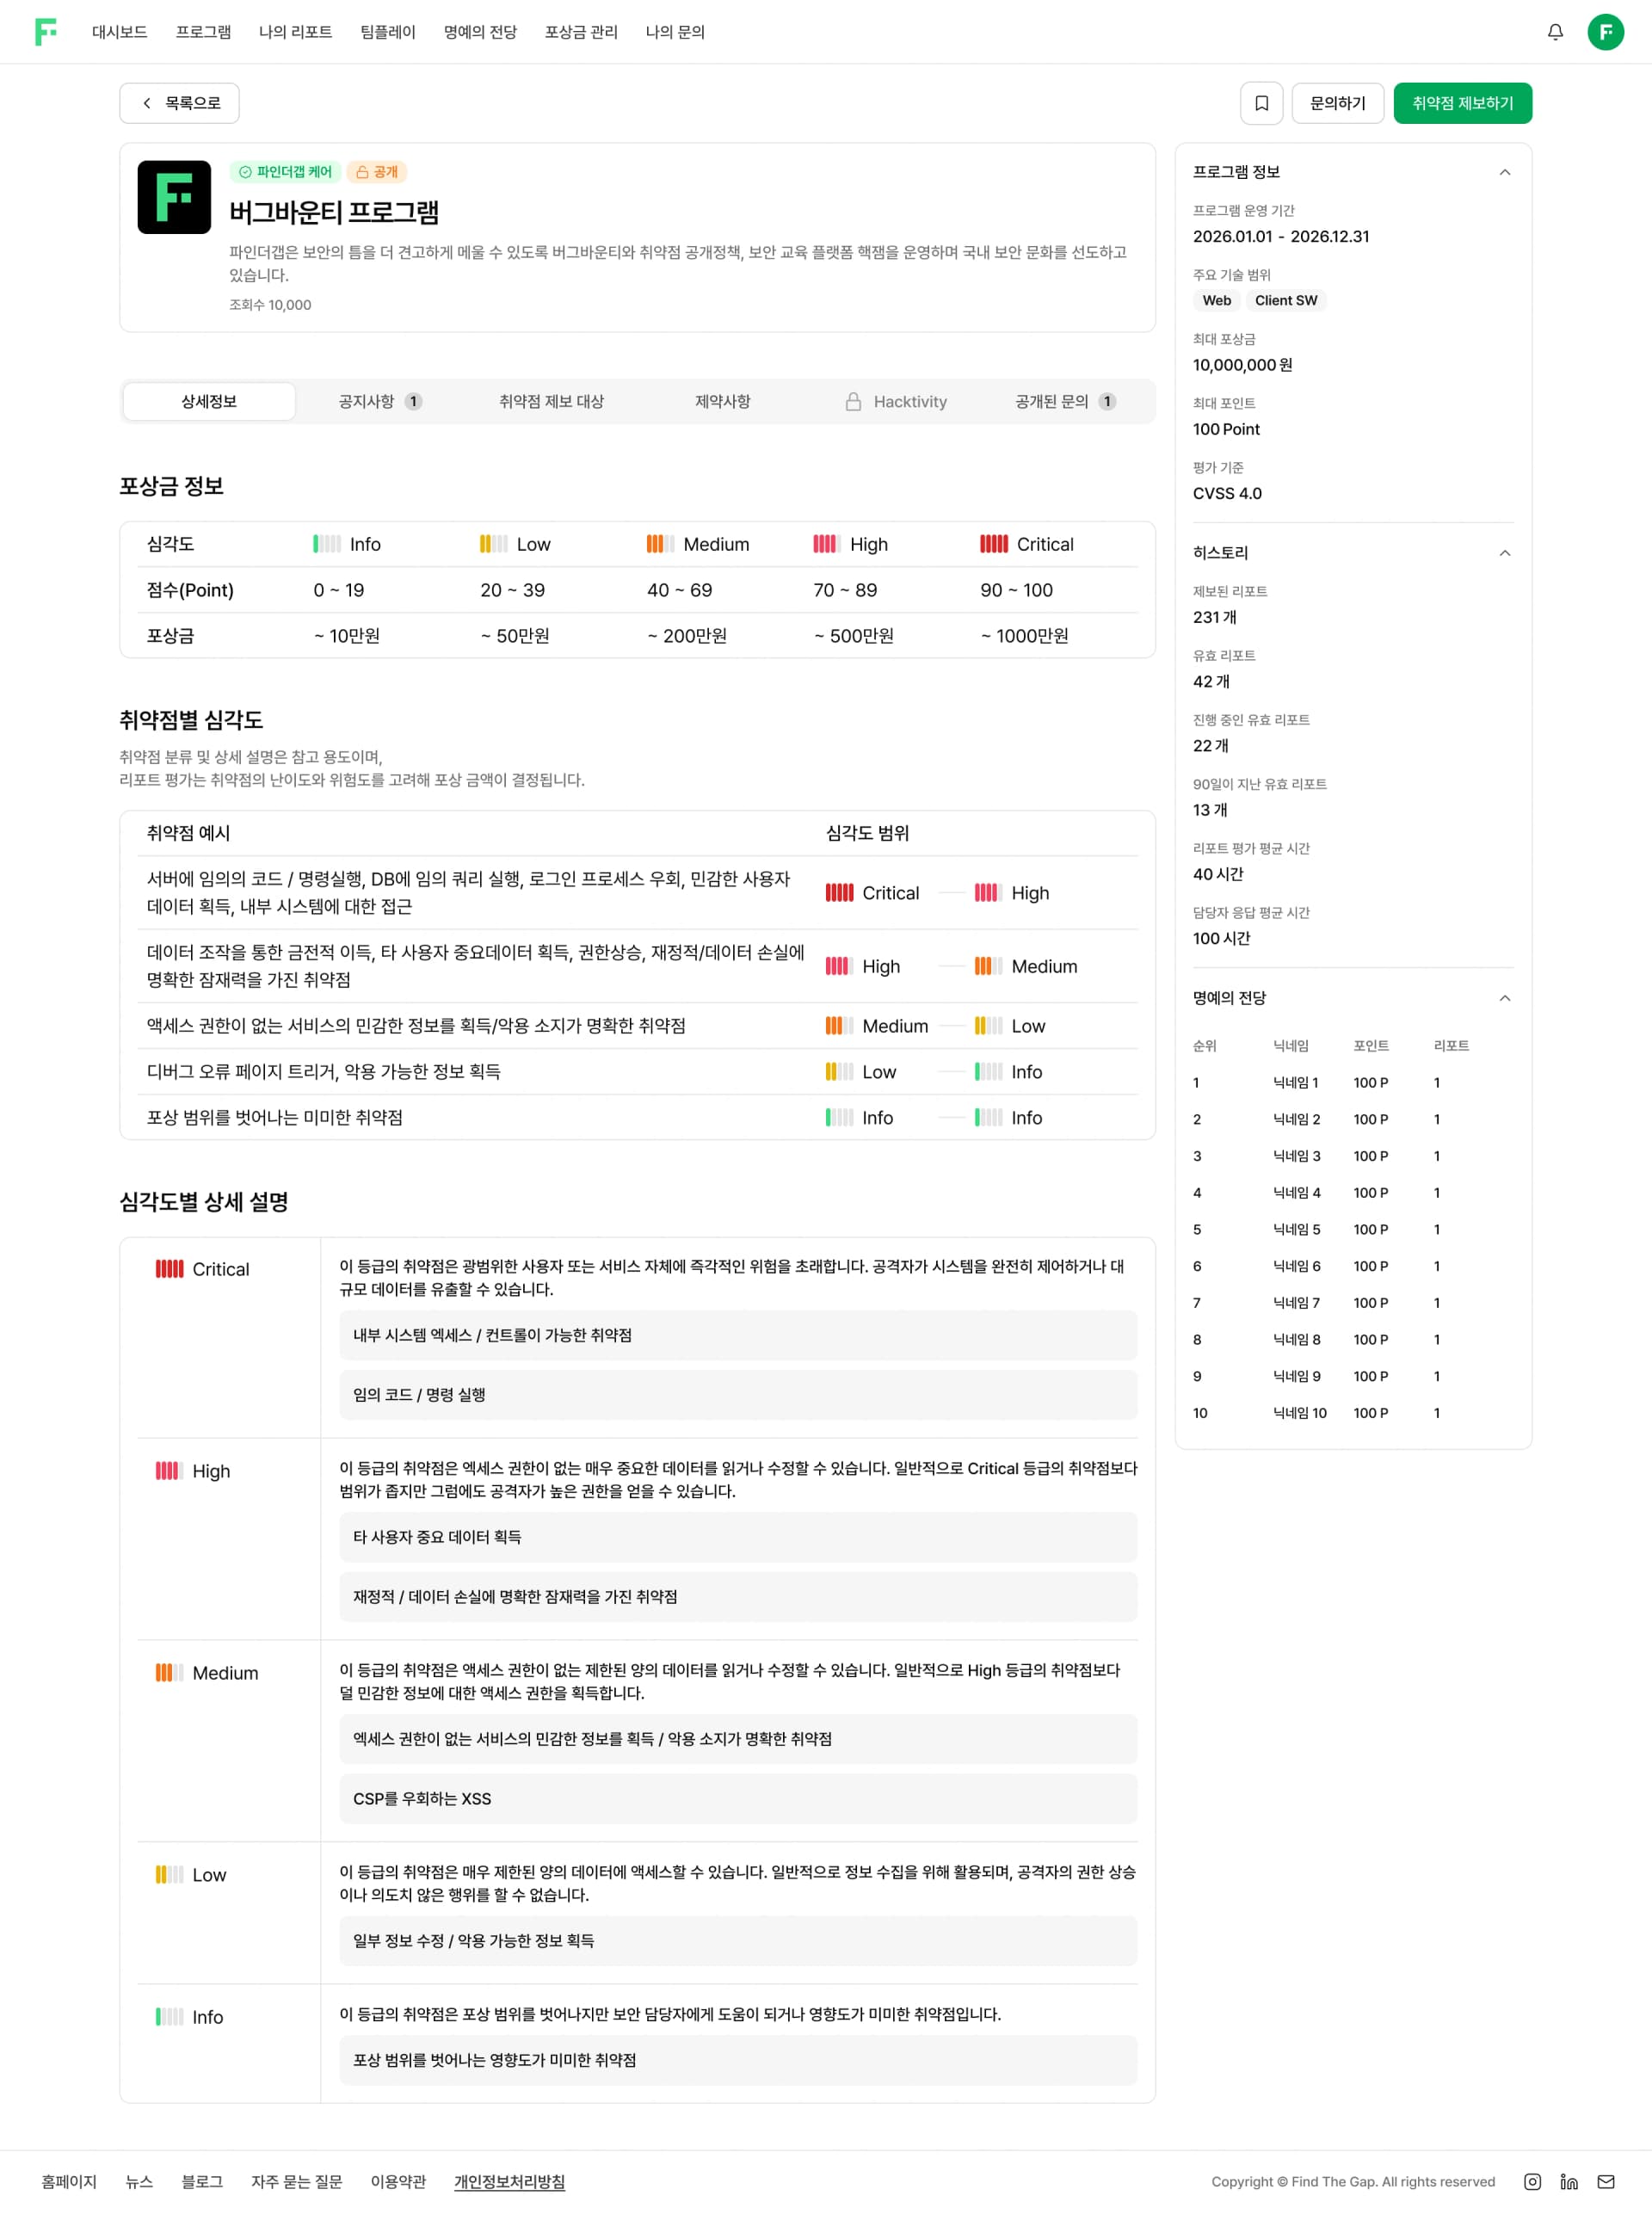
Korea's largest network of ethical hackers analyzes your institution's systems from multiple angles. Going beyond the limits of a fixed workforce, thousands of eyes are the first to spot hidden 'gaps.'
With a system running 24/7/365, the average time to the first vulnerability report is just 10 minutes. We fill the gaps between periodic audits with seamless real-time monitoring.
Find the Gap directly verifies every report to eliminate duplicates and noise. Security officers can maximize response efficiency by focusing solely on 'valid threats'.
Simulating creative attack methods of real hackers without constraints on manpower, tools, or time. We complete your defense system by finding 'live' vulnerabilities rather than providing formal reports.
Operated on a bounty basis tied to actual valid vulnerability reports, ensuring limited public security budgets are spent with maximum efficiency and transparency.
Operating a continuous bug bounty program to fill the gaps in periodic audits is a clear indicator of an institution's proactive security commitment and systematic vulnerability management.
Simple Operation without Complexity
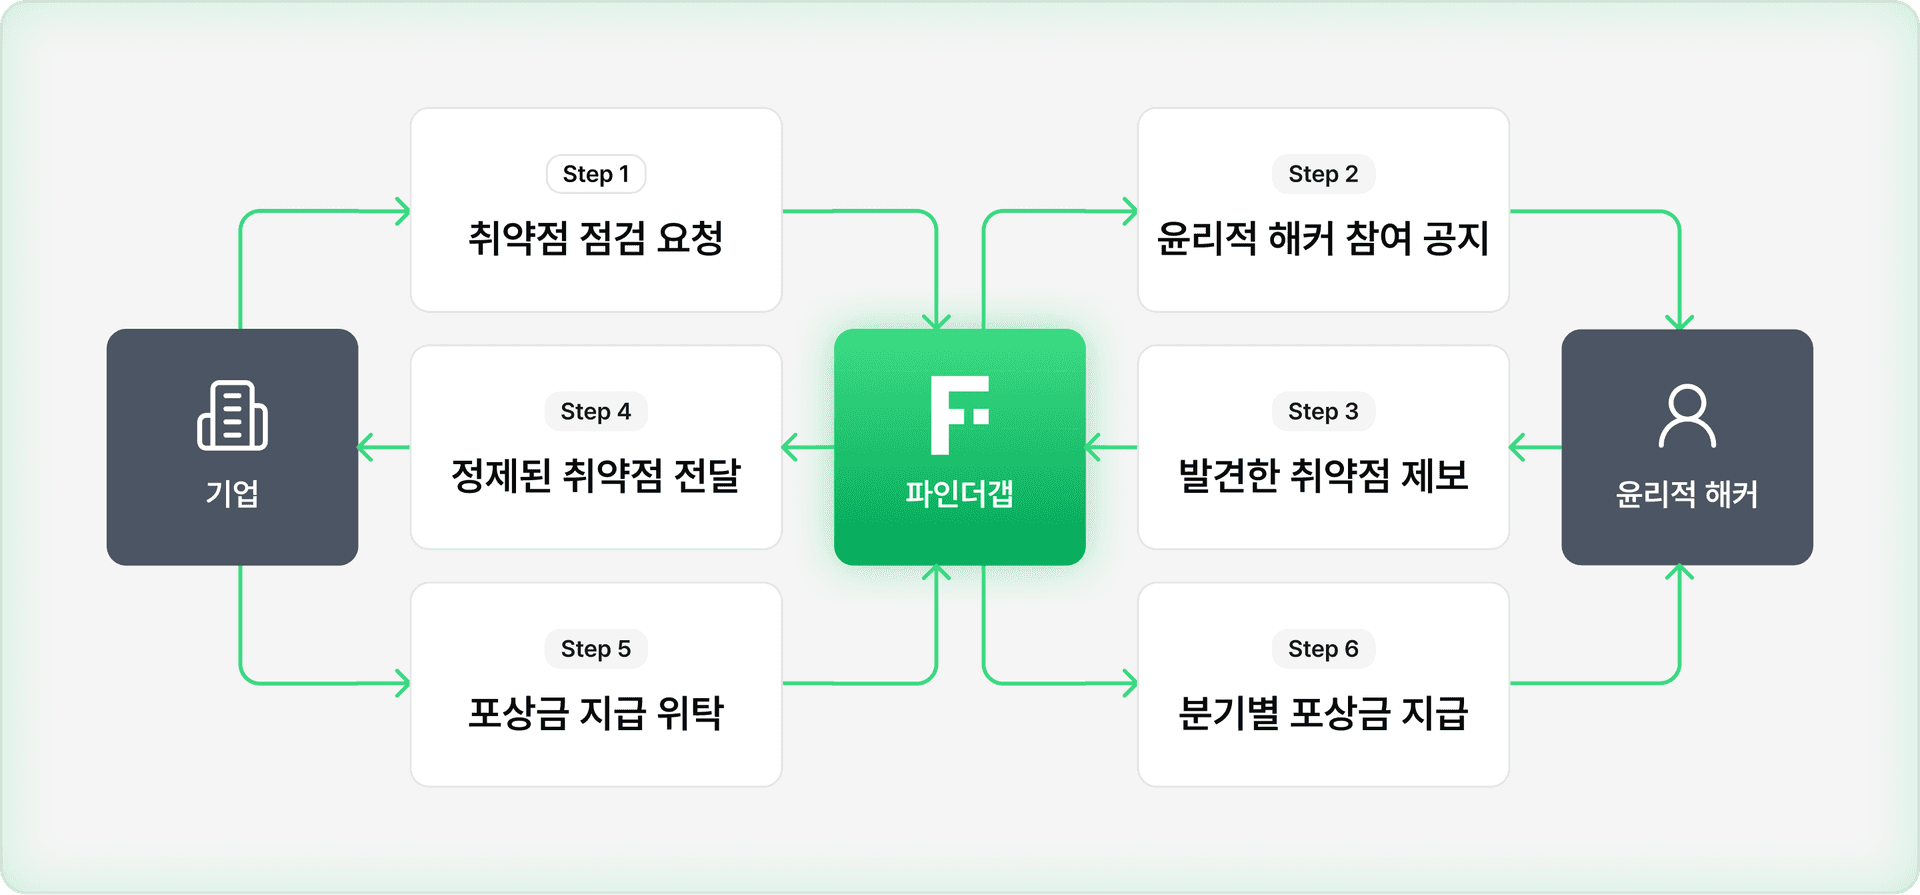
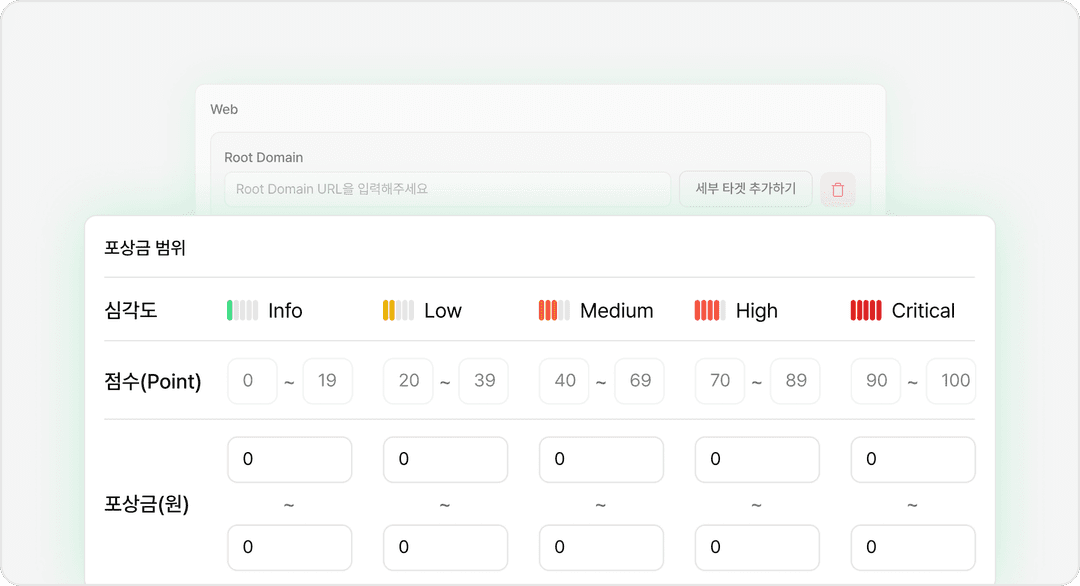
Set audit scopes and bounty guidelines tailored to your institution and services with Find the Gap experts.
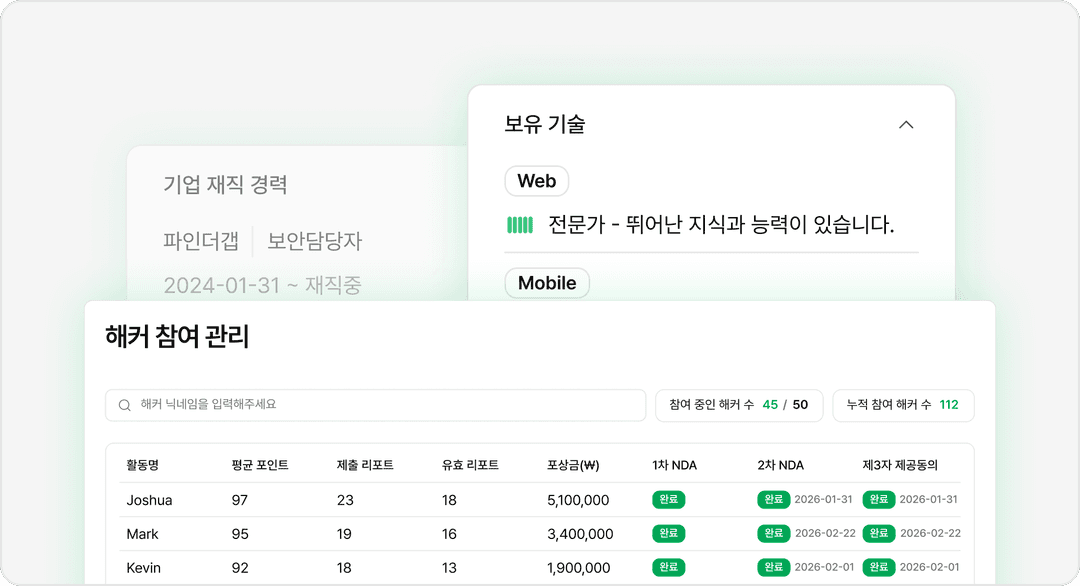
A group of experts optimized for your project's nature is selected from our 7,700 verified ethical hackers.
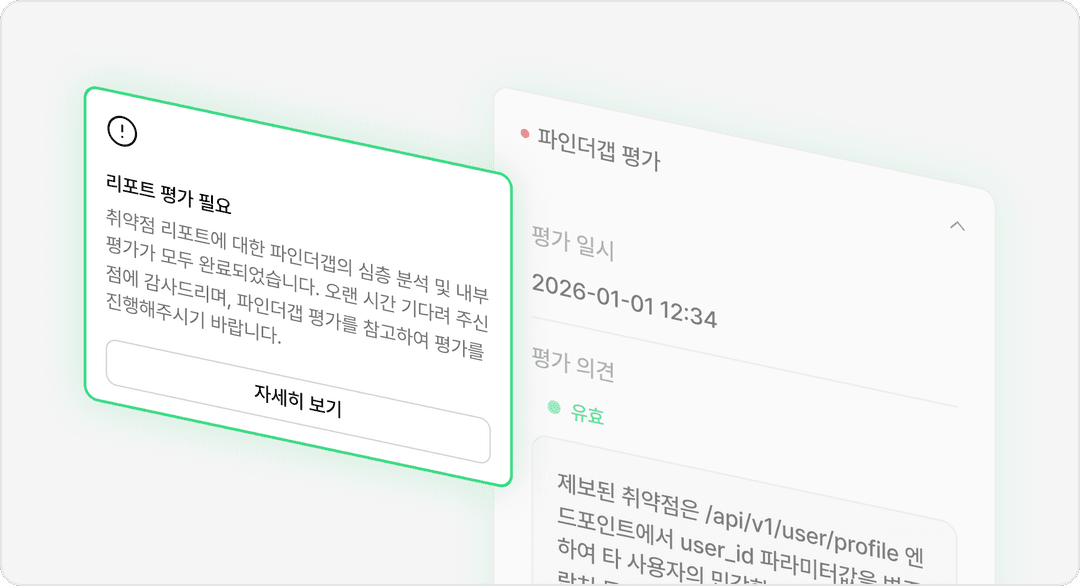
Find the Gap security experts provide primary verification of ethical hacker reports to eliminate noise.
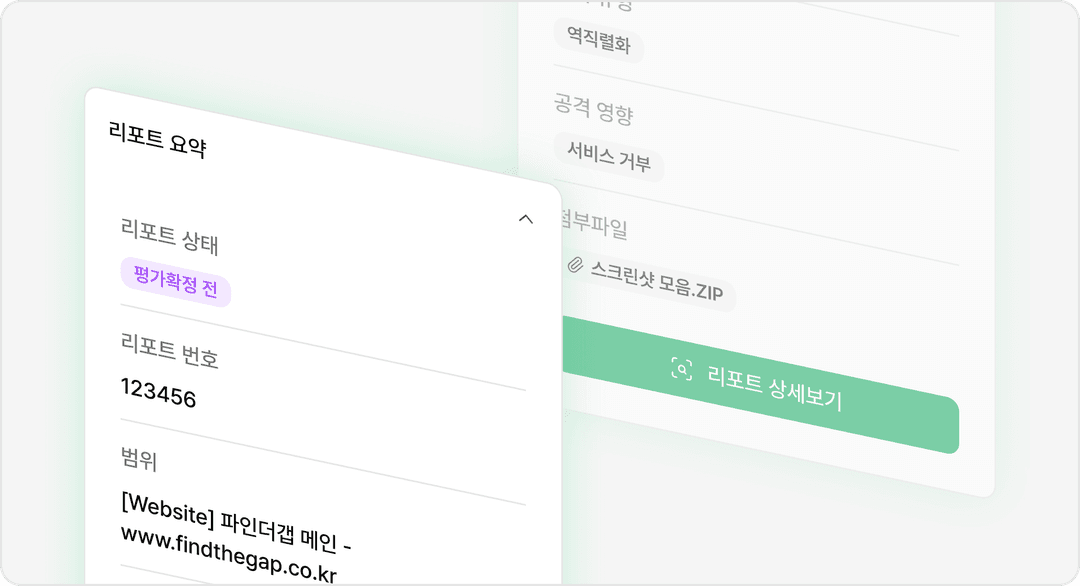
Immediately review high-quality reports that are deduplicated and include detailed remediation steps.
Synergy of AI and Collective Intelligence
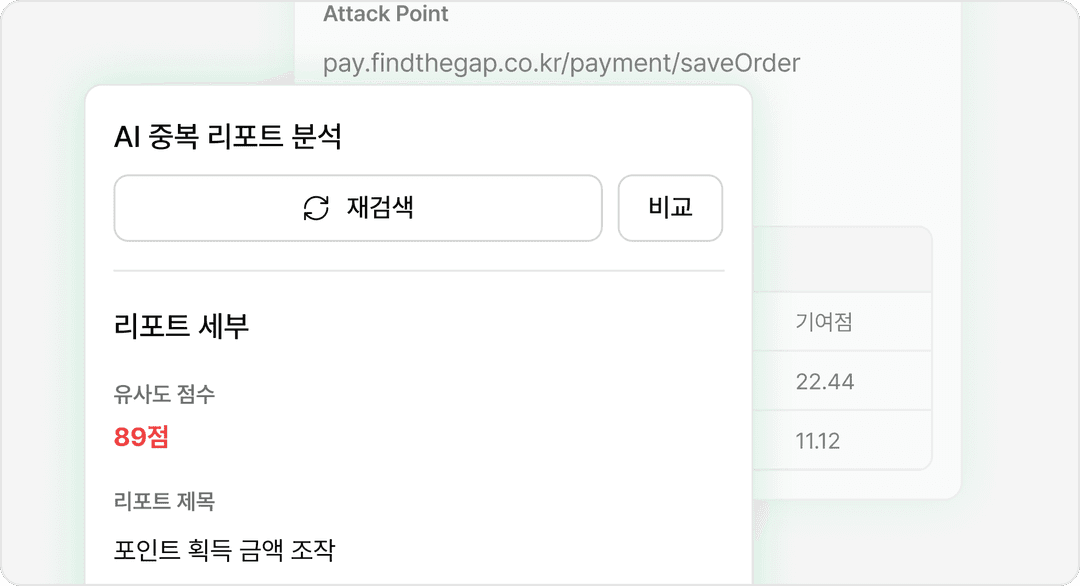
AI identifies identical vulnerabilities in real-time among hundreds of submissions. Officers no longer need to waste time on duplicate reviews.
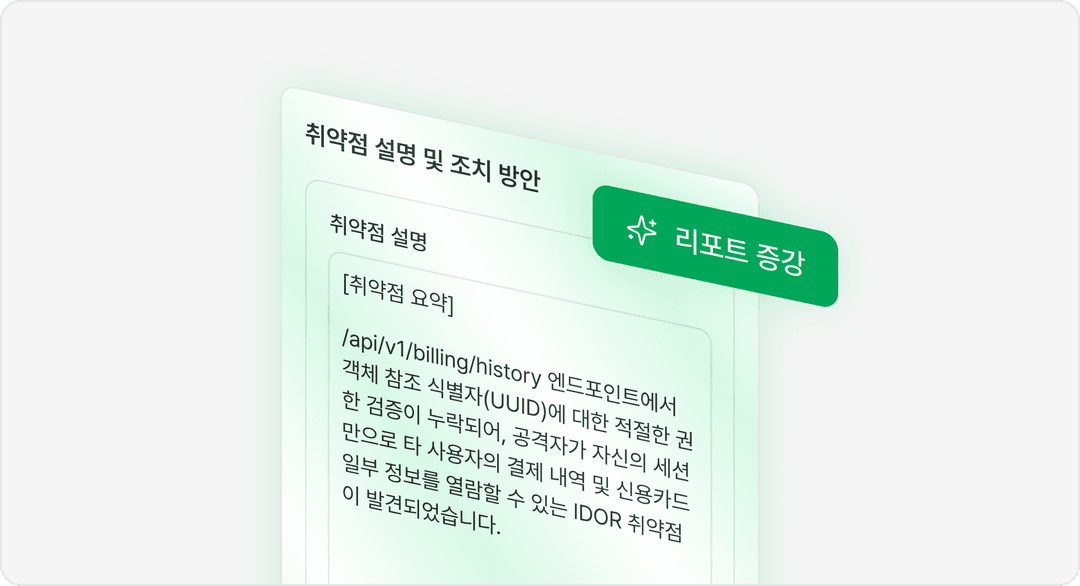
Find the Gap AI enhances the readability and logical structure of low-quality reports, refining them into high-quality documentation that is immediately actionable for institutional staff.
Secure Infrastructure and Scalability
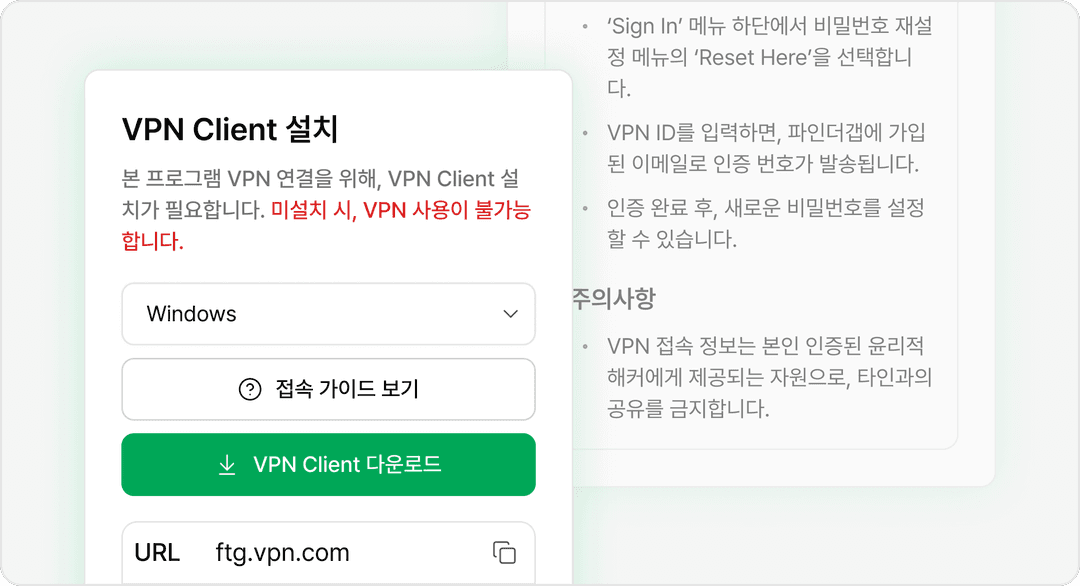
Strictly control auditor access and scope through dedicated VPN and Virtual Desktop (VDI) environments, providing safe testing tailored to internal and restricted networks.
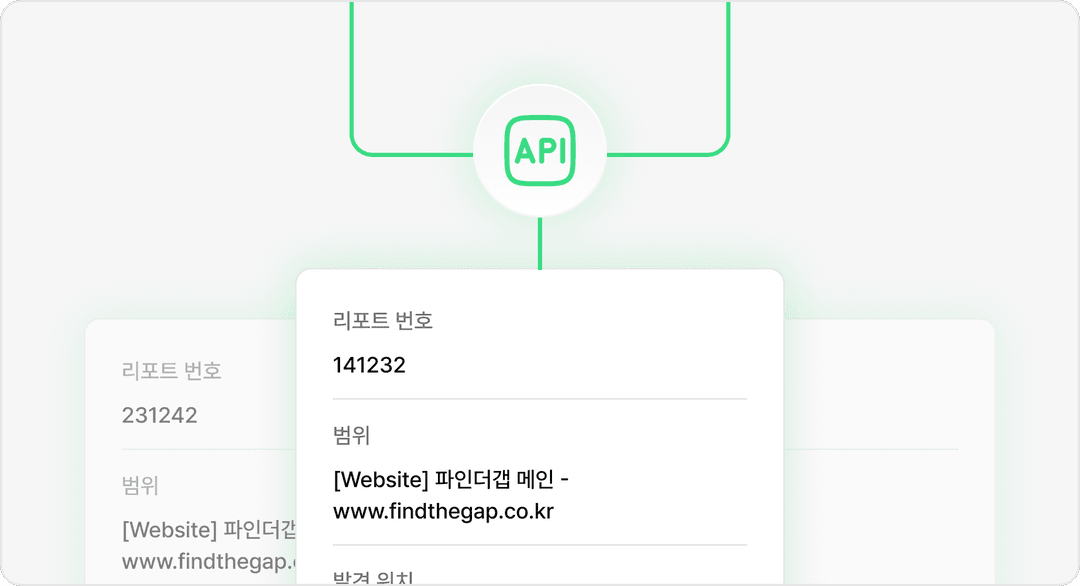
Integrate with existing collaboration tools and institutional security management environments to receive vulnerability information and generate tickets in real-time without needing to log into a separate platform.
Complete Security Visibility
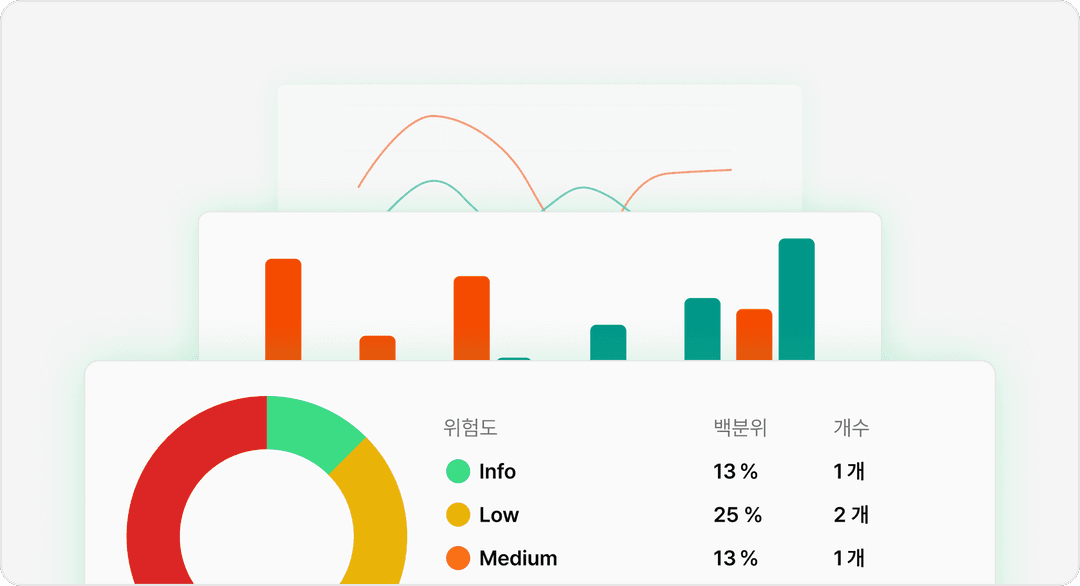
Visualize vulnerability severity distribution, average remediation time, and ethical hacker activity to use for leadership reporting and security strategy formulation.
7,700
9,600
170
"It felt like having an extra security manager on the team."
Ji-hoon Gong, Security Manager at Rappolabs
"We were able to verify security audit results at a low cost."
Byung-hee Lee, CISO at Travel Wallet
"It was an opportunity to re-evaluate security vulnerabilities we hadn't even considered."
Ki-dong Park, Information Security Team at Genesis Lab
To help both ethical hackers and corporate managers quickly find answers, we've consolidated existing FAQ notices into a single location.
For fully private programs, invitation emails are sent after a comprehensive review of platform activity history, technical skills, awards, and work experience. For semi-public private programs, participants with higher activity scores are prioritized for a separate invitation email or are approved after submitting a participation request. Therefore, the more thoroughly you update your strengths in [My Page > Career Management], the higher your chances of receiving an invitation or participation approval.